No confidential workflows
Cloud AI exposes your private data flows to the labs’ staff, reviewers, subcontractors, lawyers.


Wisp’s private architecture lets nobody (including us) read, store or train on
your data. No promises - you can verify it yourself.
The problem
Cloud AI exposes your private data flows to the labs’ staff, reviewers, subcontractors, lawyers.
Enterprise AI plans still expose your data in plaintext. Zero data retention policies are promises you just have to trust.
Agents now want your files, tools, credentials. Poor harness design leads to data leaks.
Our approach
Built with cryptographic proof that nobody can read, store or train on your data.
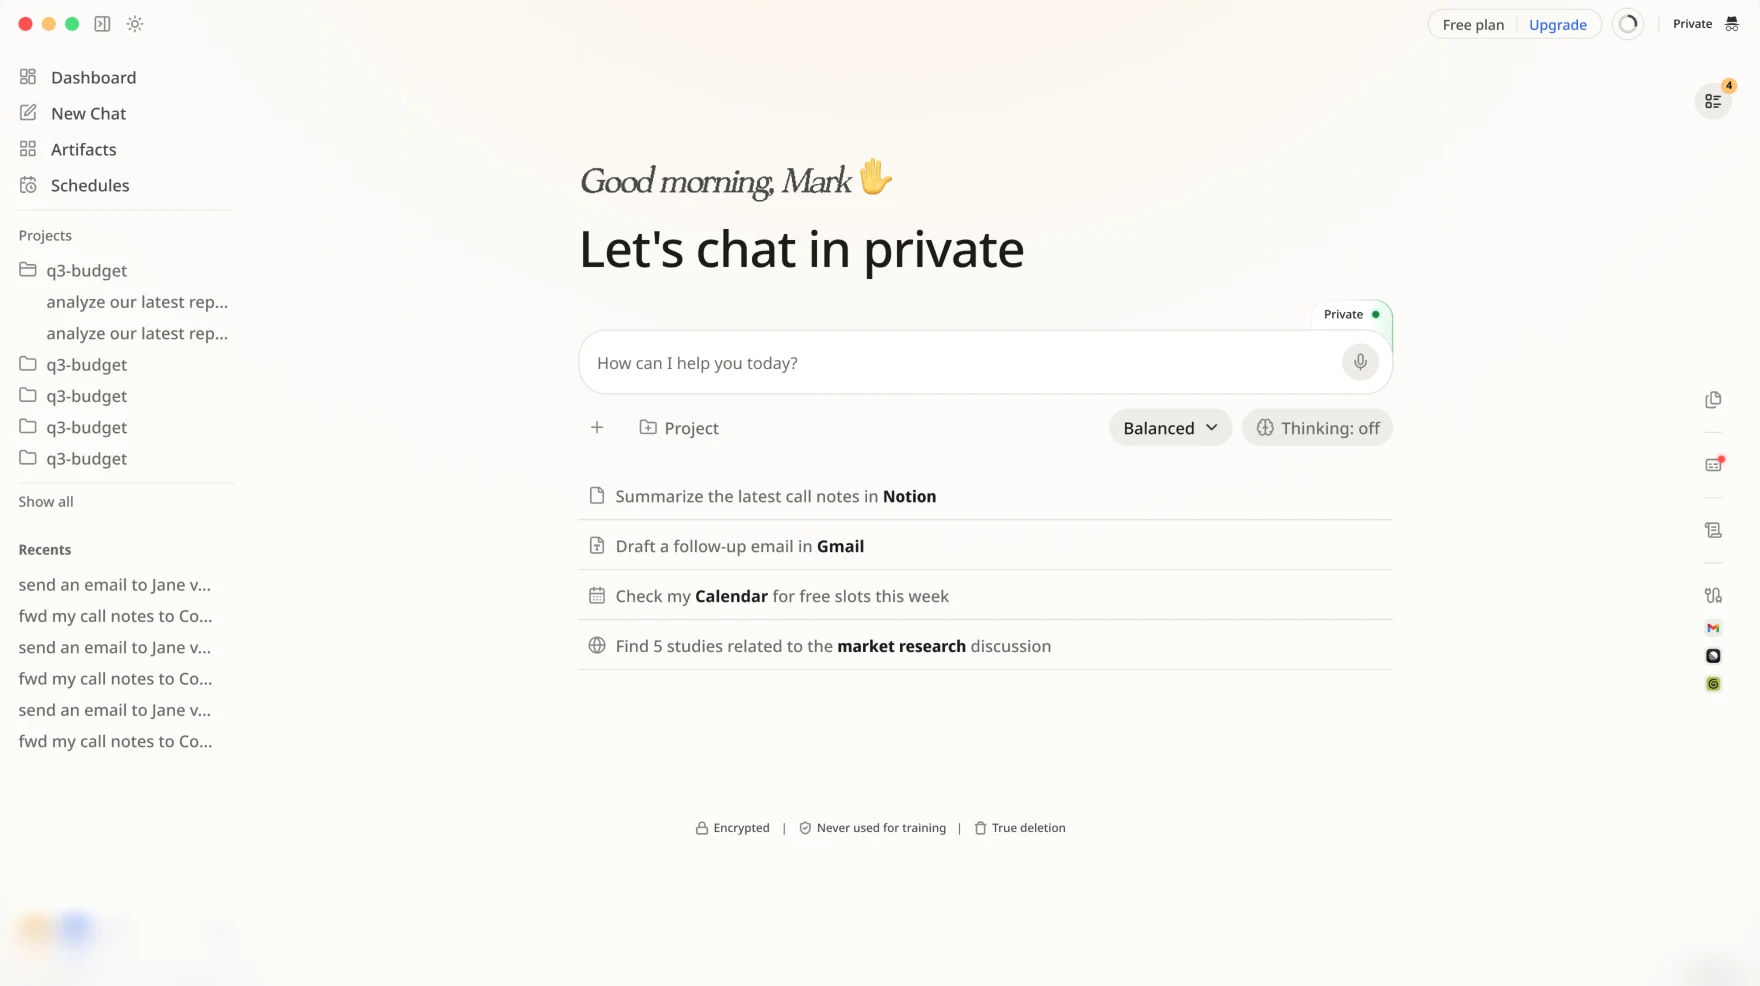
The agent, its memory and your chats live on your device, encrypted.
AI runs in a Trusted Execution Environment (TEE). Nobody, not even us, can see inside.
Hard limits on what any tool call can do. Stops the agent from misbehaving.
Runs web searches for you, so Google and other sites can’t profile you.
How it works
01

Encrypted on your machine. Data only stored locally.
 Sealed Hardware (TEE)
02

Masks your identifiable requests (e.g. web search).
03

Nobody - even Wisp or the AI provider - can see inside.
Features
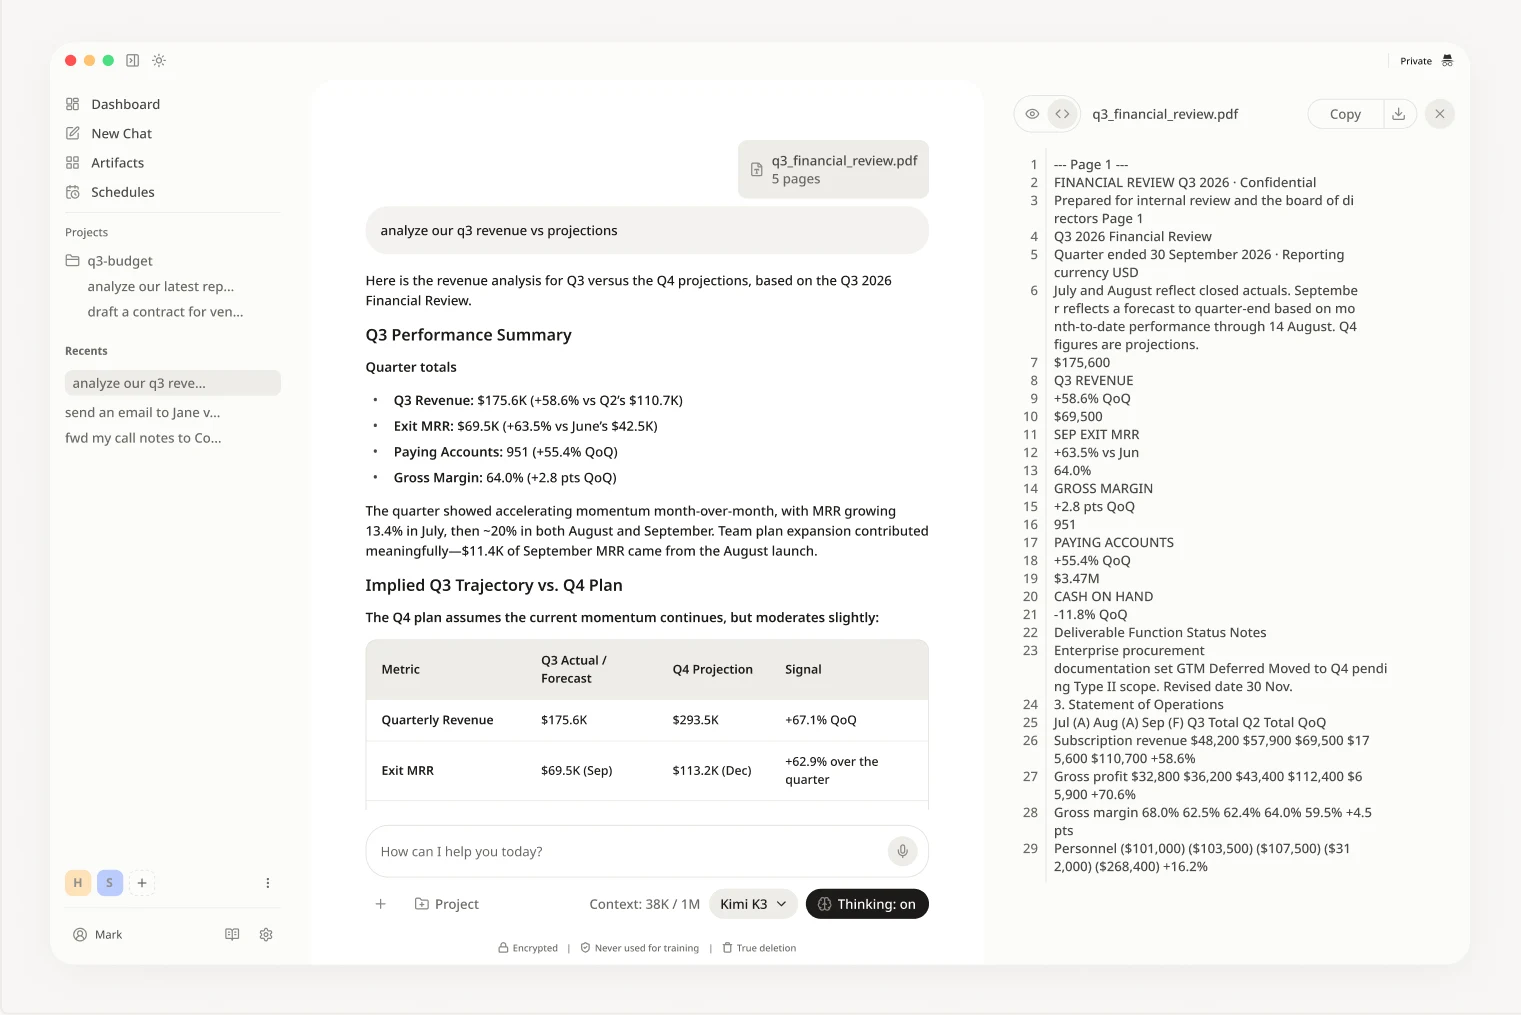

Talk freely or build projects with the Wisp Agent on Mac, Windows, Linux and mobile. On desktop it runs locally and uses only your pre-approved files.

Run the Wisp agent from your terminal or a server. Schedule jobs and get results in Telegram or Slack, with every run verifying the enclave first.
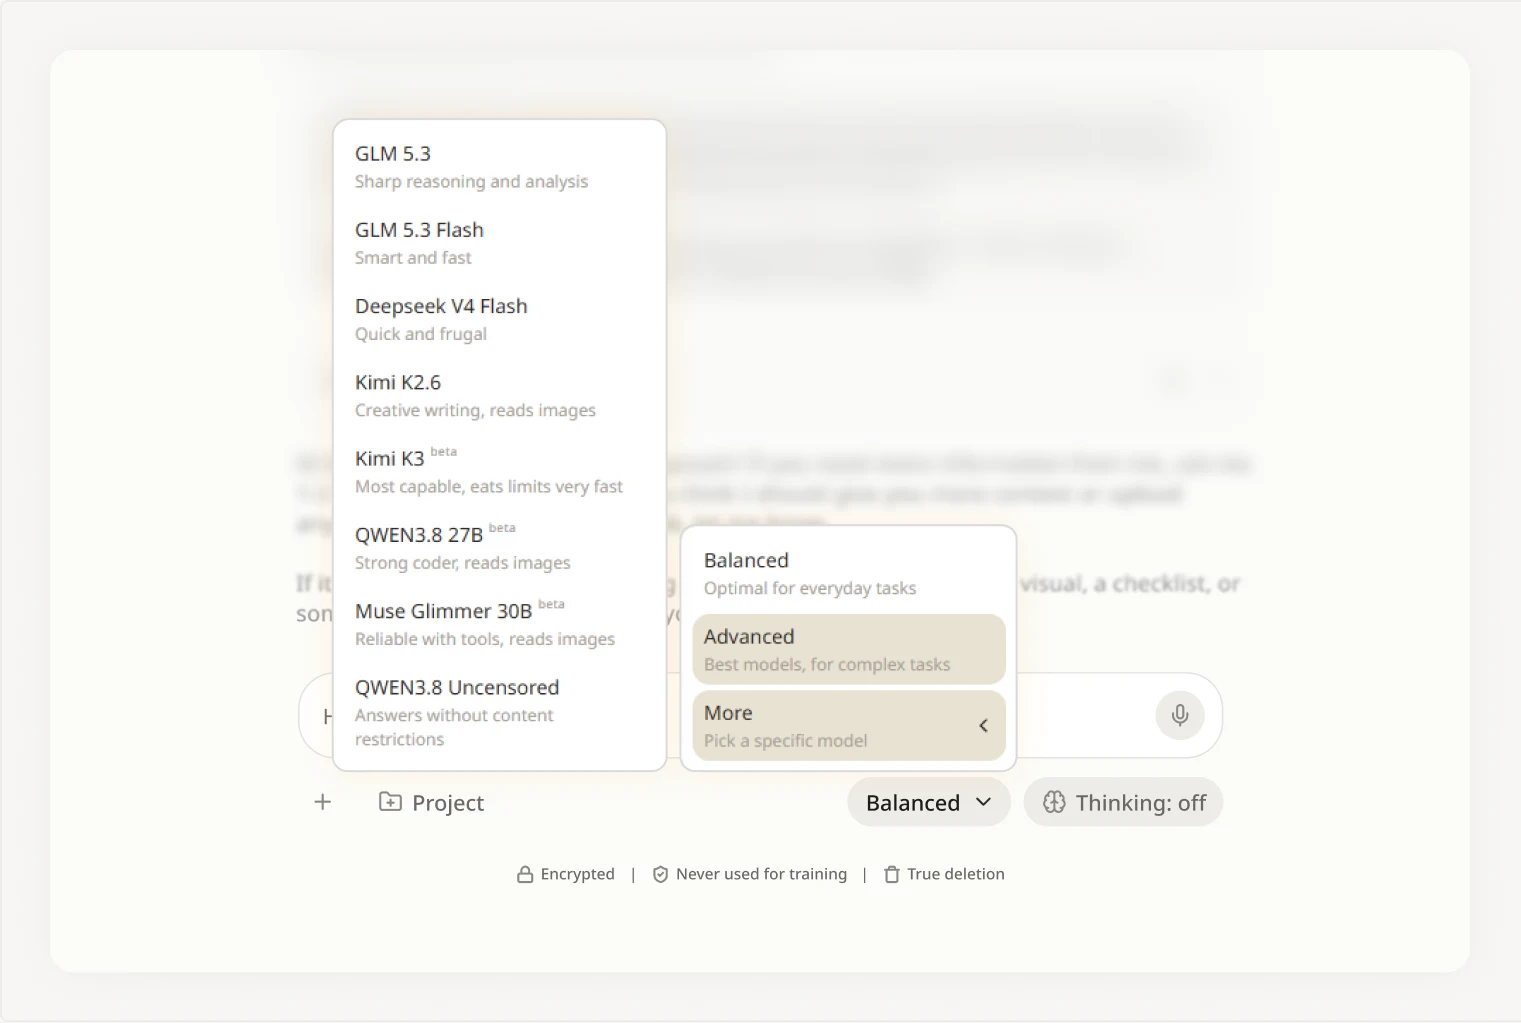

GLM 5.3, Kimi, Deepseek and other open-weight LLMs, served inside a Trusted Execution Environment (TEE)
Security
Wisp runs AI inside sealed hardware.
To prove its code, AI hardware sends cryptographic receipts to your Wisp app.
No receipt = nothing leaves your machine.
Live cryptographic attestation
Checked before anything leaves the laptop. Your team can verify the same values themselves.
Use cases
Client files, board discussions, executive messages. Nothing is logged by the AI provider.

Audit prep, budget forecasts, cap tables, quarterly reviews. All stored locally.

Competitive research, unpublished reporting, whistleblower docs. Your sources and your data stay protected.

DPAs, compliance docs, contract review. TEE-verified handling means you can prove exactly where the data went.
Why Wisp
 | Enterprise AI plans   | Banning AI(but people keep using it) | |
|---|---|---|---|
| Files stay on your machine |  |  | |
| No one at AI vendor can read prompts | | | |
| Never used to train models | | policy | |
| Anonymizes your requests | | | |
| Hardware proof, not a promise | | | |

Testimonials
“a7f3 9d2e 4c81 b6f0 e2c4 8d1a 5b9c”
“▓▒░ ████ ▒░▓█ ▒░▓ █▒░▓ ▒░▓█▒”
“xK9m R2pL qT7v N4Zb H8wF j5Yc”
We literally don’t know.
Book a demo
A live walkthrough with the Wisp team, built around how your company works: what stays on the laptop, what crosses into the enclave, and how attestation works.
 A real workflow from your team, run in WispArchitecture deep-dive for security, IT and legalA pilot plan for one team before you roll out wider
Bringing a technical colleague? Add them as a guest when you book. No time that works? Email us at contact@usewisp.io.
FAQ

No. The agent, its memory and your chats live encrypted on your device, and prompts are only decrypted inside sealed hardware that nobody, including us, can see into.
Every enclave produces a cryptographic attestation of the exact code it is running. Wisp checks it before anything leaves the laptop, and your team can verify the same values themselves. If the build doesn’t match, nothing is sent.
Not in the messaging-app sense: a model has to read a prompt to answer it. Prompts are encrypted on your machine and on the way, and only decrypted inside the enclave. The property Wisp offers is end-to-end verifiability: your machine checks the hardware before it sends anything.
No tool can do that on its own. Wisp gives your compliance team evidence of where data went and who could read it. We’ll go through your requirements in the demo.
Wisp runs leading open-weight models such as GLM, Kimi and Deepseek inside the enclave. The demo runs a real workflow from your team, so you can judge for yourself.
We start with a pilot for one team, then plan the wider rollout with your security and IT leads.
Tell us what you have in mind when you book a demo and we’ll walk through it.
It depends on your team and how you’ll use Wisp. We’ll go through it in the demo.
Switch from “trust us” to privacy by design. Only on Wisp.